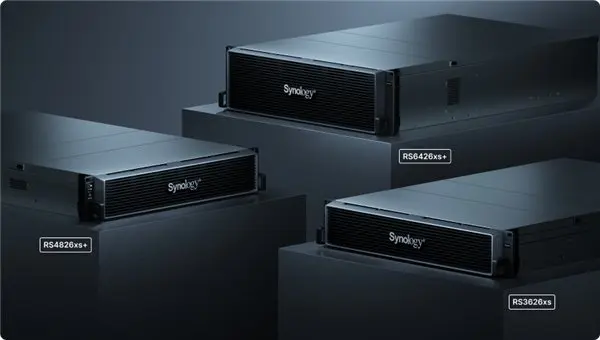
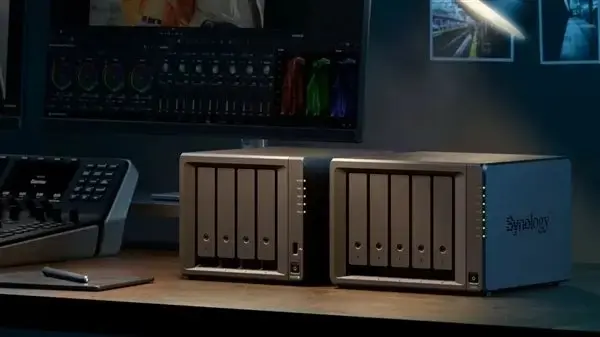
Beware! Synology NAS devices under attack. There is a live threat to synology devices where it encrypts your data with .L0CK3D (ransomware) extension.
Attackers use GitLab and PHP flaws to encrypt files with unbreakable RSA-4096 keys
The reason this is important is the attackers are looking for exposed Docker or native packages to get remote code execution! It's time to act fast and save your data. Encrypting is strong and as of this moment unbreakable without the attackers key.
The threat is linked to some specific vulnerabilities within DSM OS & it's software stack. Entry points for remote code execution issues are GitLab containers and PHP MailStation packages. The threat is verified by Synology in their advisory: Synology-SA-26:14. Which forces some updates for certain DSM versions.
Files are getting locked by a combination of RSA-4096 and AES/ChaCha20 encryption. Meaning without the private key from attackers, there is no way to decrypt the data. This threat chain is using CVE-2024-10441 along with some other critical vulnerabilities in their stack.
Synology forces updates to DSM 6.2.4-25556-8, DSM 7.1.1-42962-7, DSM 7.2-64570-4, DSM 7.2.1-69057-6 and DSM 7.2.2-72086-1. Some people still get infected by versions higher then the threshold of safe DSM version numbers. We recommend to pull out the network cable and disable backup services to stop lateral infection.
To patch for this threat, the following are required as well. BSM 1.1-6574, DSMUC 3.1.4-23079. Synology recommends immediate actions to lock down your device against this large scale attack. Please double check your DSM version and patch it as soon as possible!
The advisory lists specific minimum versions like 7.2.2-72086-1 for DSM. If my unit is on 7.2.1-69057-6, does that mean I am still vulnerable even though it is only one minor build behind?
Yes. The attack chain relies on CVE-2024-10441 and the specific GitLab/PHP RCE flaws. You need to update to at least 7.2.1-69057-6 or higher to get the patched components. Pull the network cable until you can apply the patch.
pulling the network cable is basically bricking the nas for remote access tbh 😅
The RSA-4096 encryption makes recovery nearly impossible without the key. This is why offline backups are the only real defense against this level of crypto locking.
Synology also mandates updates for BSM 1.1-6574 and DSMUC 3.1.4-23079. People often forget the underlying utility packages are part of the exploit vector too.
iirc the gitlab container was never officially supported by synology so why is it pre installed on the default package center 🤔
The article claims some users with newer versions are still infected. This suggests the vulnerability might be in the DSMUC package which is separate from the main DSM version numbers.
ngl i thought docker containers were isolated enough to prevent this kind of lateral movement. looks like the kernel exploit bypasses those limits.
The attack vector targets the PHP MailStation package specifically. If you do not use mail services on your nas you can disable that package to reduce your attack surface immediately.