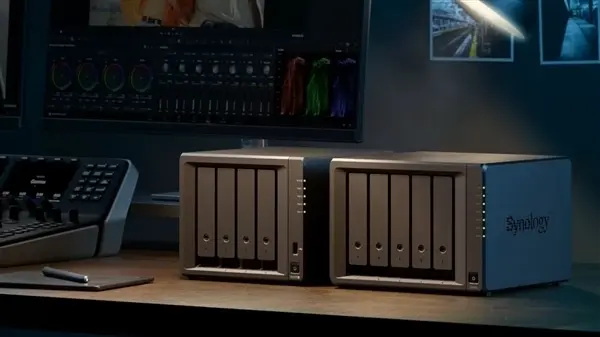
A ransomware attack, dubbed C3RB3R is specifically and actively seeking out Synology NAS devices that are not updated with the most recent security patches. The significance of this attack comes from the fact that a known vulnerability was being exploited, that Synology had patched months ago. This leaves any unprotected systems open to a data wiping attack. If you are a user who depends on this equipment for data storage, make sure that you immediately check the status of your software to avoid unauthorized access.
Synology urges users to update DSM and check Security Advisor immediately
This ransomware attack is aimed directly at the DiskStation Manager (DSM) OS installed on Synology devices. Synology explained that the issue was due to vulnerability Synology-SA-24:20 that enabled attackers to take over a system. They do confirm that this specific vulnerability was addressed in December 2024. But that means there are systems that did not apply the update and are in danger.
Synology points users to four specific actions they can take to reduce their risk of becoming infected. First, they need to perform a scan with the Security Advisor to see if there are vulnerabilities in their current setup. Second, they need to make sure that DSM and any installed packages are up-to-date with the latest version. If users have automatic updates enabled, that will help avoid any delays in applying important security updates.
The final and most important defense against ransomware encryption is off-site backup. To prevent this, they recommend Hyper Backup or Snapshot Replication to store the data in another location. This gives the user an opportunity to restore their data from a clean location even if it is encrypted by the attackers.
We did cover the last Synology NAS update with some similar themes coming out surrounding balance and stability. This attack serves as a reminder that the stability aspects need to be kept in line with the security needs as well. Synology also continues to stress to all users to be vigilant if you are utilizing NAS solutions.
Comments (0)