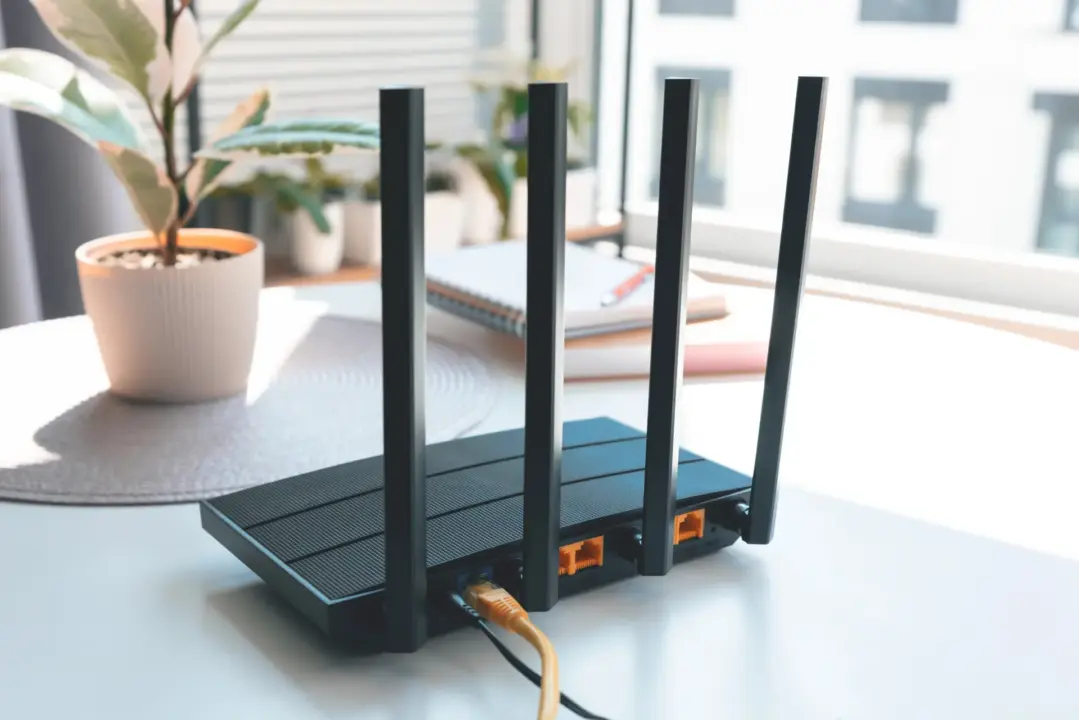
There's a 16 year old security flaw that is still active on Broadcom WiFi chips, which gives hackers the ability to remotely hack your router if you're using Broadcom WiFi chips. This is a serious security risk as it means random people can take control of your home or office network from afar. If you're a consumer or network admin using broadcom based infrastructure, this is a high priority security problem.
Hackers can still remotely control routers using a 16-year-old Broadcom Wi-Fi chip flaw
The specific flaw that is present in Broadcom WiFi chip design that has been around for years. It's an issue where attackers can take advantage of this bug to remotely hack routers and get admin access over it. This would allow them to use it as a tool to hack other networks. This is a major security vulnerability as it breaches the first line of defence for the router which are the authentication protocols.
This security flaw has been around for 15 years and it's still affecting current hardware on the market. The fact that this flaw has been around for so long may indicate that there might be some old code structures or compatibility needs that are preventing a complete fix on newer hardware. Also the fact that the bug is still active means that if you're using those specific Broadcom chips on a device, that device could be vulnerable until patched.
You need to check if you're using broadcom WiFi chips on your current router/access point to see if you're vulnerable to this specific threat. The risk of being remotely hacked is high until a patch or firmware update by the vendor comes to fix the vulnerability. You may need to put in some temporary defences to protect your network or replace your devices if they don't release a software patch.
Discussion
0 comments
Log in to join the thread with a thoughtful take, question, or correction.