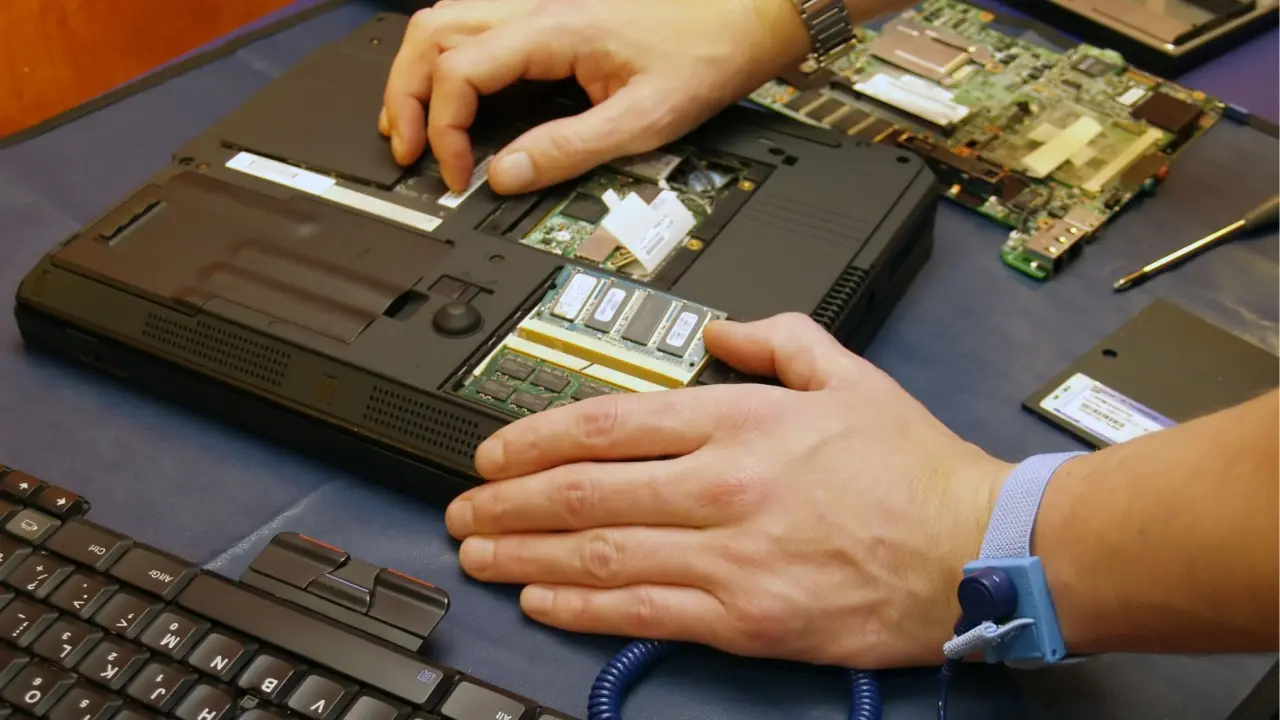
With this $10 hardware tool now available you can bypass the supervisor password on older generation Lenovo ThinkPad laptops. This exploit gives a new life to the decommissioned business laptops avoiding the e-waste. If you purchased one of those 4th-8th gen Intel locked laptops, now you can unlock them without hiring any professional.
Cheap hardware tool unlocks older business laptops
The technique exploits the Embedded Controller (EC) and BIOS firmware specifically on these generations of ThinkPads. Researchers identified the EmulatedEepromDxe driver is allowing read and write unauthorized access to the EEPROM chip. This access vector is key for attackers to modify the password stored in the controller.
- Compatible CPU Generations: Intel 4th- to 8th-generation
- Required Hardware Tool: CH341A programmer
- Software Utility: NeoProgrammer
- Vulnerable Component: Embedded Controller (EC) / BIOS
The exploit gained traction on YouTube (via Hileeq) with the use of CH341A programmer and NeoProgrammer tool. You will need to physically plug the programmer into the laptop motherboard in order to directly patch the BIOS. The root vulnerability was reversed-engineered by Mark Juvan for his cybersecurity master’s thesis at Radboud University.
The technique is limited to ThinkPads with Intel processors from 4th to 8th generation. The exploit is based on a specific implementation of the driver in the older firmware. Physical access to the laptop along with the required programming tools are needed to perform the bypass.
The technique provides a valuable way to recover locked enterprise hardware. It allows to turn the decommissioned laptops into useful working units for personal or educational use. The vulnerability is still a serious security issue for the companies that manage these older asset classes.
Does this EC patch actually clear the supervisor password permanently or does the BIOS revert on a CMOS reset?
The EmulatedEepromDxe driver writes directly to the EEPROM chip. A CMOS reset only clears volatile RAM. The password persists until you flash a clean EC image.