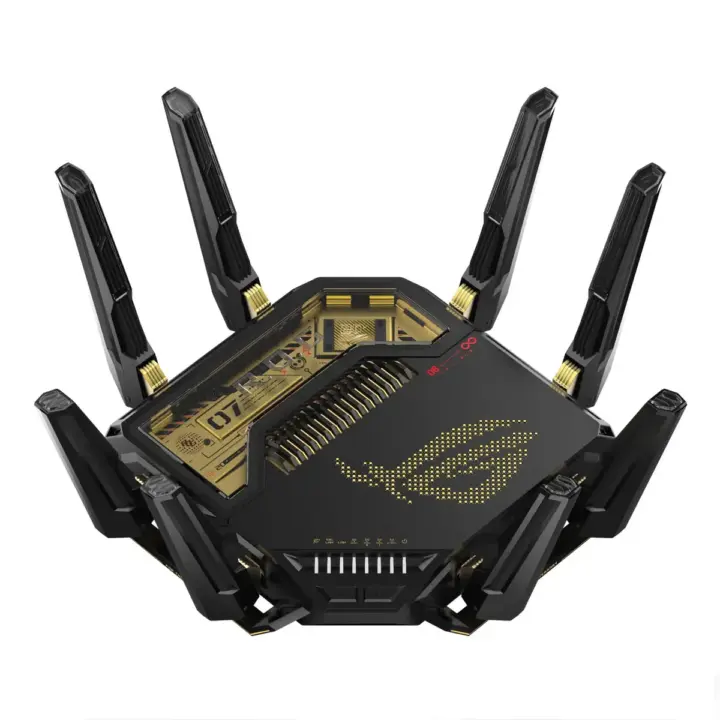
ASUS has just dropped an urgent firmware update for their Wi-Fi 7 routers. They've patched a serious security hole. Here's why you should care: this vulnerability lets hackers on nearby networks completely skip over your security measures.
ASUS releases emergency patch for authentication flaw in Wi-Fi 7 routers
For those of you using these routers to connect your home or small business, it's a direct threat. Unauthorized access is right around the corner. Don't wait-make sure to update as soon as possible to plug this hole in your network security.
The problem? An authentication bypass bug in the router software. Hackers can take advantage of this and get full admin rights without even needing the correct login.
That's right, someone in wireless range could have full control of your network settings and data. These routers are on firmware series 3.0.0.6_102 at the moment.
Here's what ASUS recommends in the meantime: block remote access (WAN) immediately. Make sure all admin passwords are strong and unique to minimize exposure. Don't forget, after applying the firmware patch, you'll need to reboot your system to make the changes take effect. While doing that, watch for any unknown devices on your network to confirm the fix is working.
This is an emergency patch aimed at a particular vulnerability with high risk to connected devices. This update fixes the authentication bypass that enabled unauthenticated access. Check your firmware version and if it's the affected series, update immediately. It's crucial to keep your router's firmware up-to-date to secure your network.
Discussion
0 comments
Log in to join the thread with a thoughtful take, question, or correction.