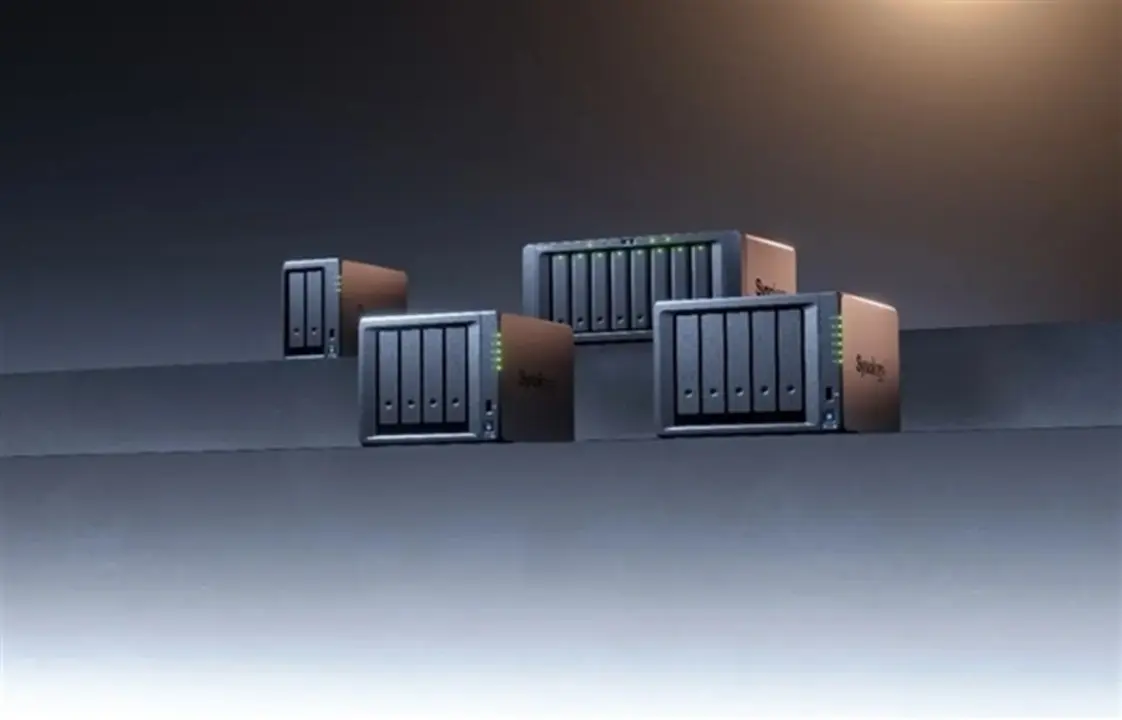
Synology on November 10, 2024 released a critical security patch for their DiskStation Manager (DSM) operating system. With this patch, they are fixing two major vulnerabilities that can give an attacker access or the ability to destroy your data on your network storage. Users should immediately apply the fix as Synology didn't offer any workarounds to address these vulnerabilities.
Synology urges immediate DSM updates to prevent data destruction
Synology has published their security advisory Synology-SA-26:19 addressing vulnerabilities in the main software for their NAS devices. DiskStation Manager is the control system for their network storage appliances and this makes it a huge target for attackers. This makes updating to this critical patch necessary for anyone using affected versions of DSM to ensure system integrity.
One of the vulnerabilities has a CVSS score of 9.8, which means that it can allow a remote attacker to read/write arbitrary files and service denial. The other vulnerability has a CVSS score of 8.6 and can lead to unauthorized file access and service denial. Both vulnerabilities have the same root problem with code that can cause threats to confidentiality and availability of your data.
Synology recommends that everyone should review their current build number of their DSM and update to the newest version immediately. Synology has not offered any workaround to temporarily address the issues, so the only solution is to apply the patch. This patch is critical to close the security issues in your network storage that could potentially be exploited.
Synology-SA-26:19 is out. The 9.8 CVSS score on the arbitrary file access vulnerability means your data is exposed if you are running older DSM builds. You need to check your build number right now.
no workarounds available, so the only fix is the patch itself. scary that a 9.8 score just gives remote write access 😂