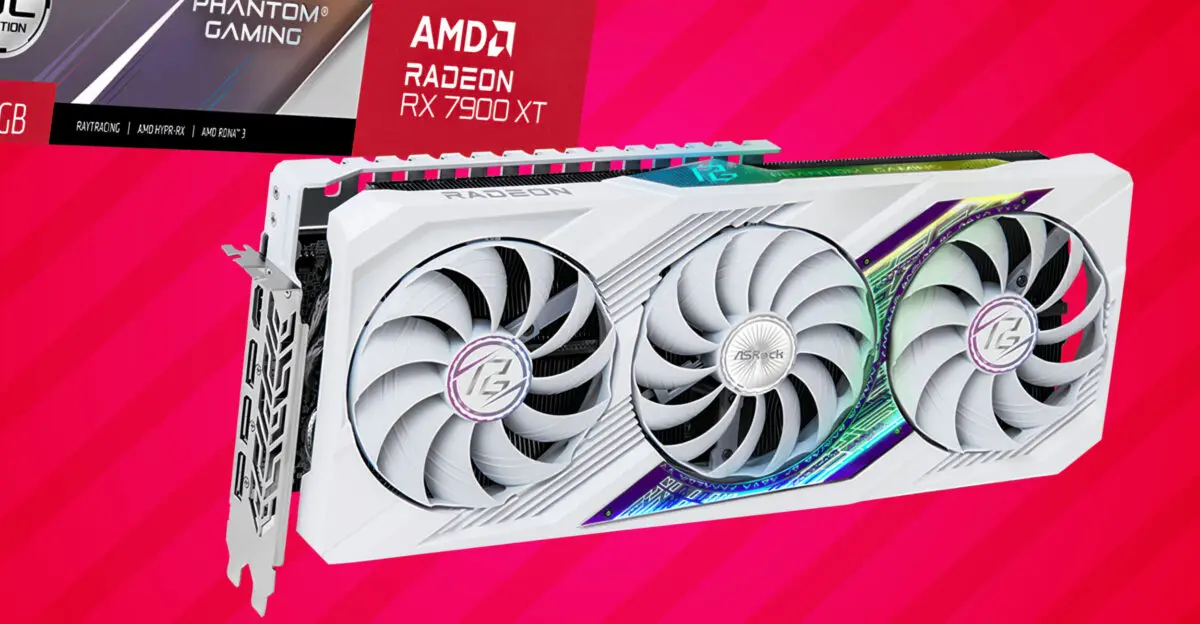
ASRock issued new VBIOSs for 10 Radeon RX 7000 GPUs to fix potential security issues. It's important because people who have these specific GPUs should install the patch to make sure they are safe from potential (unconfirmed) exploits. So make sure to verify if your GPU model is part of the list, to keep it safe.
ASRock releases VBIOS updates for Radeon RX 7000 graphics cards to fix potential security issues
The list of GPUs affected is quite extensive, as the new VBIOSs are meant to fix potential security issues on various Radeon RX 7600 XT, RX 7700 XT, RX 7800 XT, RX 7900 XT, and RX 7900 XTX models. Affected are Challenger, Steel Legend, Phantom Gaming and Taichi models in multiple colors. So the bulk of high-end and mid-end AMD GPUs from ASRock are getting fixed in this case.
ASRock identifies these new downloads as ASRVBFlash version 1.0.5. All 10 affected models were updated to 1.0.5 on October 29, 2026. We don't know whether this 1.0.5 version is just for the flashing tool or also for the VBIOS (firmware) that is flashed on the GPU.
AMD did not provide any details in public or any technical information. So we have no idea what exactly this security flaw is all about. This follows similar VBIOS releases by Sapphire and Gigabyte earlier this month. Seems like the industry is working together to fix something on a hardware level.
We have covered ASRock Teases Radeon RX 9070 XT in our previous Asrock coverage, so you can see that they are developing things. However, in this case, we are getting a new VBIOS that's meant to keep things safe instead of adding new features. This confirms that they are working to maintain their current line of Radeon RX 7000 GPUs.
ten models just for a security patch that nobody knows about yet
Does the ASRVBFlash tool verify the digital signature before flashing or can it be abused by malware in this specific window
The utility typically checks the vendor signature against the embedded certificate in the VBIOS image. If the signature does not match or is missing it will refuse to write to the chip
I am not downloading a flashing utility from a support page to fix a ghost vulnerability. I will wait for a signed driver package that includes the firmware
at least they are not charging for the fix like the subscription GPU folks
Sapphire and Gigabyte did this too so the industry is likely patching a common AMD silicon level issue