Lenovo is fixing some major security vulnerabilities with their ThinkPlus storage products. Lenovo admits that many of their USB fingerprint drives with popular 'encrypted' storage is mostly all hype. This is an important issue for consumers who were trusting these drives to secure their important data. Lenovo is now rolling out new firmware and even replacement plans to help fix the security concerns in several different models.
Lenovo rolls out firmware updates and hardware replacements for affected storage models
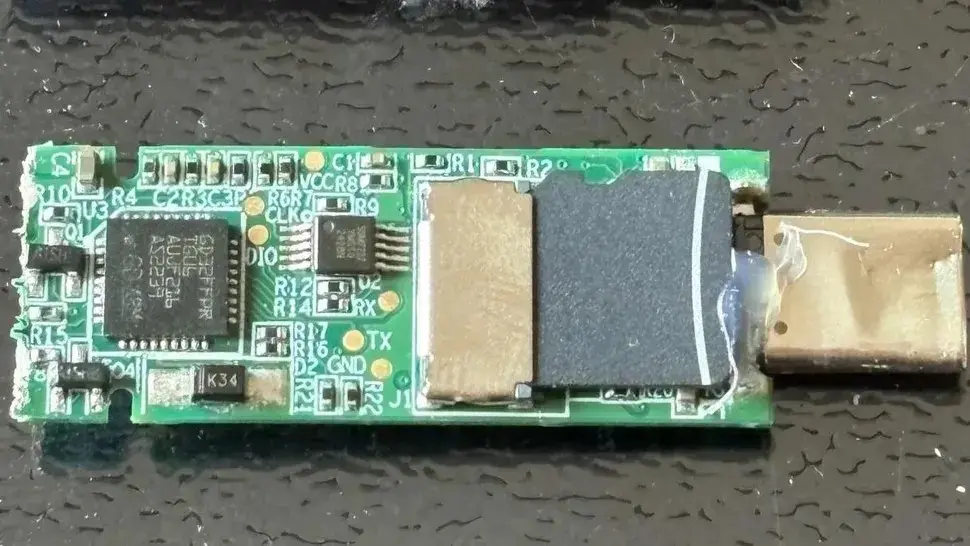
The main problem is with the ThinkPlus FU100 model which was advertised as supporting AES-256 encryption. Security experts found out that it's just an ordinary SD card, not encrypted, inside a fancy casing. The fingerprint reader is only used to allow access to the USB interface for your computer. This means the data stored on the SD card is completely vulnerable to software based attacks.
The FU100 is not the only model that has some security concerns. Lenovo found other issues with the FU200, TU800, TSD303 SSD's. Specifically the TSD303 SSD models were sending passwords to the host software in plain text.
That made it very easy to get the passwords from a potential hacker. This issue was classified by Lenovo as a high severity security advisory. This means they've made changes to help consumers right away.
Security expert Xu Cheng Li pointed out that Lenovo is selling the FU100 model as just an SD card in a fancy case. Xu Cheng Li said that all of the hardware security features were just marketing fiction. Security experts used AI tools to find hard coded keys and backdoors for other security USB products for several different manufacturers.
Lenovo is now pushing new firmware updates and even a replacement program for the affected FU100, FU200, TU800, TSD303 models. If you own one of these devices you should either update to the new firmware or you can reach out to get a hardware replacement. This new update should fix the plain text password sharing and non-encrypted storage concerns from the security audit.
Comments (0)