
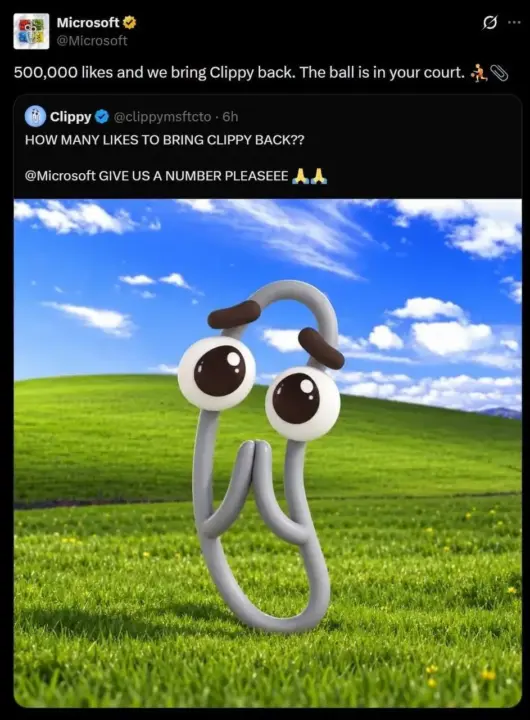
Microsoft's official X account was compromised for about 30 minutes on October 3, 2024. This incident matters because it shows how quickly a major tech brand's public voice can be hijacked for financial scams. Users should be cautious of any sudden promotional posts from verified accounts that promise unexpected rewards or cryptocurrency investments.
Attacker used fake Clippy return promise to promote fraudulent cryptocurrency token
The breach involved the @microsoft handle on the X platform, formerly known as Twitter. An attacker gained unauthorized access to the account and used it to publish a post. The message claimed that the classic Clippy assistant would return if the post received 500,000 likes. This was a tactic to drive engagement for a fraudulent cryptocurrency token named $Clippy.
Microsoft spokesperson Brent Colburn confirmed the security breach in a statement. He stated that the company verified unauthorized access to their account running on X servers. The attacker successfully published content that was not written by Microsoft staff. Microsoft has since secured the account and deleted the unauthorized posts.
The company is currently investigating the extent of the breach. Microsoft explicitly denied any association with the $Clippy cryptocurrency. The company also announced that it is taking legal action regarding the incident. This response aims to protect users from further confusion or financial harm related to the scam.
Discussion
0 comments
Log in to join the thread with a thoughtful take, question, or correction.